
 timothyandClaude Opus 5
5d46ea150f
#853 asked whether Gitea 1.27.1 can restrict `workflow_dispatch` by ref, or gate a
secret behind a protected environment, and warned against closing the issue by
asserting the trust boundary without probing option 3 first.

Probed across every surface rather than stopping at the endpoint the issue already
knew 404s:
  - `CreateActionWorkflowDispatch` takes `ref` as a REQUIRED free-form string, with
    no allow-list or pattern field, and no repo/org/admin endpoint scopes it.
  - Protected environments do not exist at 1.27.1 — 0 of 308 documented API paths
    contain "environment"; secrets are org/repo/user-scoped only.
  - `/api/v1/settings/actions` 404 reproduced; host `[actions]` config carries only
    ENABLED + DEFAULT_ACTIONS_URL; no `gitea admin` subcommand touches actions,
    runners or secrets.

So option 3 is unavailable. But the probe also found why the answer does not rest on
that: dispatch is NOT the narrowest route. `docker-build.yml` triggers on
`pull_request:`, which Gitea resolves from the PR head, and its `test` job carries no
event guard, is the required context `Build & test (.NET) (pull_request)`, and logs
into the registry with REGISTRY_PASSWORD. "Push a branch, open a PR" therefore reaches
the same credential with one FEWER deliberate act than a dispatch. Restricting
dispatch alone would close the more visible of two routes and change nothing.

Accepted on that reasoning rather than on "repository write access is the boundary" —
the issue's own leading option, and the one to reject: it is unfalsifiable as stated
and it hides the cheaper route.

Also measured, because it is easy to misread the existing records the other way: the
write set is exactly `timothy` (admin) and `renovate` (write, NOT admin). The merge
gate bounds what Renovate can MERGE; nothing bounds what it can RUN. A matched probe
with anonymous and authenticated-non-writer controls shows `renovate` passes the
dispatch authorization gate — an authenticated non-writer short-circuits with
"not found", while `renovate` here reaches ref resolution like a known writer does.

Not applied here, deliberately: `tag_protections` is empty and a `v*` rule would close
docker-build.yml's tag row against the bot. That is live protection-class config whose
failure mode is a broken release cut, so it needs its own change and its own
verification. Tracked with the `pull_request:` residual in #885.

fixes #853

Decisions-Edit: yes
Co-Authored-By: Claude Opus 5 <noreply@anthropic.com>
Claude-Session: https://claude.ai/code/session_01UYNbVwgVszv6Pum7ZuGd75
ErsatzTV
ErsatzTV lets you transform your media library into a personalized, live TV experience - complete with EPG, channel scheduling, and seamless streaming to all your devices. Rediscover your content, your way.


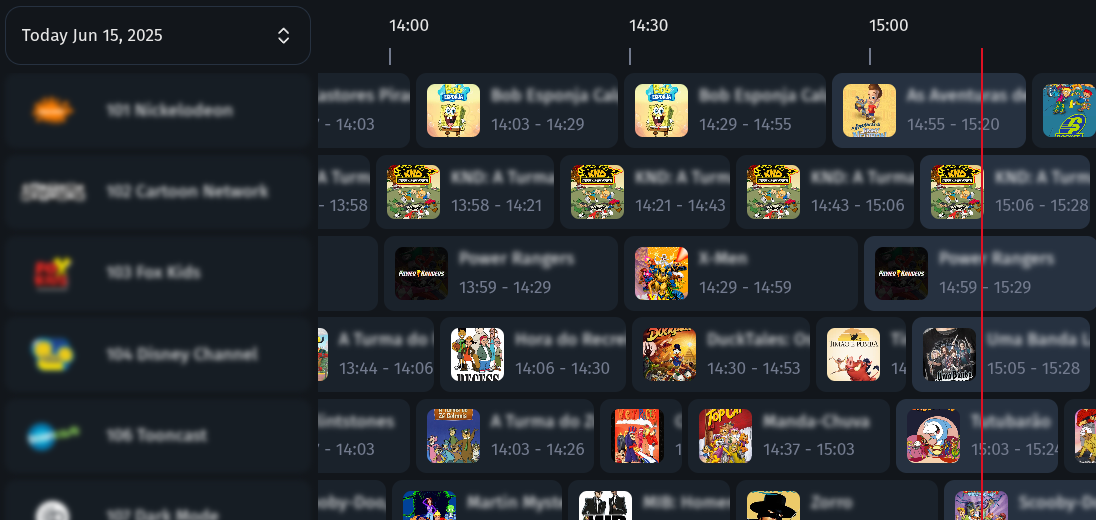
How It Works
- Install ErsatzTV: Download and set up the server on your system.
- Add Your Media: Connect your media libraries and collections.
- Create Channels: Design and schedule your own live channels.
- Stream Anywhere: Watch on any device with IPTV and EPG support.
Key Features
- Custom channels: Create and schedule your own live TV channels.
- IPTV & EPG: Stream with IPTV and Electronic Program Guide support.
- Hardware Transcoding: High-performance streaming with hardware acceleration (NVENC, QSV, VAAPI, AMF, VideoToolbox)
- Media Server Integration: Connect Plex, Jellyfin, Emby and more.
- Music & Subtitles: Mix music videos and enjoy subtitle support.
- Open Source: Free, open, and community-driven project.
Documentation
Documentation is available at ersatztv.org.
License
This project is inspired by pseudotv-plex and the dizquetv fork and is released under the zlib license.