 timothy
4196a057fb
Build ErsatzTV Image / CI toolchain image resolves (pull_request) Successful in 10s
PR Gates / CI image pin matches docker/ci (pull_request) Successful in 13s
PR Gates / Docs update reminder (pull_request) Successful in 16s
Build ErsatzTV Image / Delimiter ban (release path) (pull_request) Successful in 22s
PR Gates / decisions lifecycle (pull_request) Successful in 17s
Review verdict / Set review-verdict status (pull_request_target) Successful in 16s
PR Gates / Fix proofs (Proves trailers) (pull_request) Successful in 16s
PR Gates / Script lint and tests (ruff + pytest) (pull_request) Successful in 5m12s
Build ErsatzTV Image / Build & test (.NET) (pull_request) Successful in 8m35s
Build ErsatzTV Image / EF migration integrity (SQLite + MySql) (pull_request) Successful in 6m20s
Build ErsatzTV Image / Build & push image (amd64) (pull_request) Skipped
Build ErsatzTV Image / Functional E2E (curl + UI contracts) (pull_request) Successful in 5m56s
Build ErsatzTV Image / API docs in sync (OpenAPI + endpoint index) (pull_request) Successful in 7s
Build ErsatzTV Image / Formatting (changed .cs conform to .editorconfig) (pull_request) Successful in 5s
review-verdict/h10 Review-verdict: MERGEABLE @ 4196a05 (base: main)
`actions/checkout` leaves an `Authorization` header in `.git/config` unless
`persist-credentials: false` is set — write-capable while this instance's Actions
default token permission is `permissive`, where it stands after a Restricted trial
was reverted on 2026-08-05 (#748). Every workflow here except `review-verdict.yml`
omitted it, so a job handed that credential to every script it ran, not merely to the
checkout. 15 of the repo's 16 checkouts now set it.

Setting the flag first would have been unsafe, which is why #743 deferred it rather
than doing it blind: five steps ran `git fetch ... origin "$base_ref" || true` and
fed the result into changed-file skip logic, so a credential regression would have
presented as an empty changed set on the three steps that also masked `git diff`, and
a possibly-absent `origin/<base>` handed to a fail-open Python validator on the other
two — a silently self-skipping check on a green job either way.
So the masking comes out first, and only then does the flag go on. `git diff`'s own
`2>/dev/null || true` goes with it on the three sites that had one.

`--depth` came off those five fetches in the same step, and that is the part the cold
reviews converged on. All five run in jobs that check out `fetch-depth: 0`, and
`git fetch --depth=N` grafts a *complete* clone shallow — measured on a 150-commit
repo branched 130 back: `.git/shallow` appears and `git diff origin/main...HEAD` fails
`fatal: no merge base`, while the same fetch without `--depth` returns the correct
file list. Under `|| true` that was a silent skip; unmasked it would have reddened
`api-docs` and `format` on any branch not rebased inside the depth window, and left
`decisions lifecycle` green with its diff-dependent checks silently skipped.

Loud is not the same as blocking. `api-docs`, `format` and `decisions lifecycle` gate
on this diff and now redden on a failed fetch. `docs-reminder` does not — it is a
non-blocking nudge whose advisory red would still join the combined status the merge
gate reads, which is why its `Set up Python` and doc-narrative steps already carried
`continue-on-error: true`. The parity nudge now carries it for the same reason, so all
three of its non-checkout steps have it and the `::error::` reaches the log without
becoming a merge block. `Checkout` stays blocking.

The population is wider than #746's file list. Sweeping the shape rather than the
named file found 8 checkouts in `docker-build.yml` (not the six #743 recorded), 5 in
`pr-checks.yml` and 1 in `dependency-scan.yml`, and three masked fetches in
`pr-checks.yml` beside the two in `docker-build.yml`. That widening is recorded on the
issue so acceptance is judged against what shipped. No job that checks out pushes with
git, and the repo is public with anonymous `git-upload-pack` answering, so nothing
loses a capability it was using. Renovate does push branches, but `renovate.yml` has
no checkout step and carries its own `RENOVATE_TOKEN`.

Two further masked fetches, in `scripts/ci-detect-docs-only.sh` and
`scripts/ci-detect-already-validated.sh`, keep their masking on purpose: in both, a
failed fetch can only leave the base revision unresolvable, and an unresolvable base
emits `false` — run the full matrix. Neither can turn a failed fetch into a skip.
Their `--depth` is a different matter and is NOT cleared here: the push-path
`--depth=2` grafts the `build` job's `fetch-depth: 0` checkout, which is why `:latest`
images ship `InformationalVersion 0.0.0-<sha>` — measured on the live test container
as `0.0.0-5a7a4ed7` and filed as #836. Four stale statements of that script's
shallow-consumer set (two in docs/ci-cd.md, one in the script itself, one in
`ci.docs-only-detect-shallow-safe`) said `fetch-depth: 1` and named two of the three
consumers; they are corrected here, because this change states the same fact
again and would otherwise leave the corpus disagreeing with itself.

`ci-image.yml`'s one checkout is the exception, and not because it is safe: its
unfiltered `push` trigger is head-resolved in the sense that matters. It is excluded
because any commit touching that file re-points `ci-image-pin`'s `expected` at itself
and reddens a blocking job, and because the same trigger would publish a toolchain
image from the editing branch. It rides with #744.

No machine-checked guard holds the convention yet: writing one now means a hardcoded
`ci-image.yml` exemption whose only justification is a temporary condition in another
issue, and that entry would outlive its reason silently. Filed as #835, blocked by
#744, to be written with no exemption list at all.

fixes #746

Decisions-Edit: yes
ErsatzTV
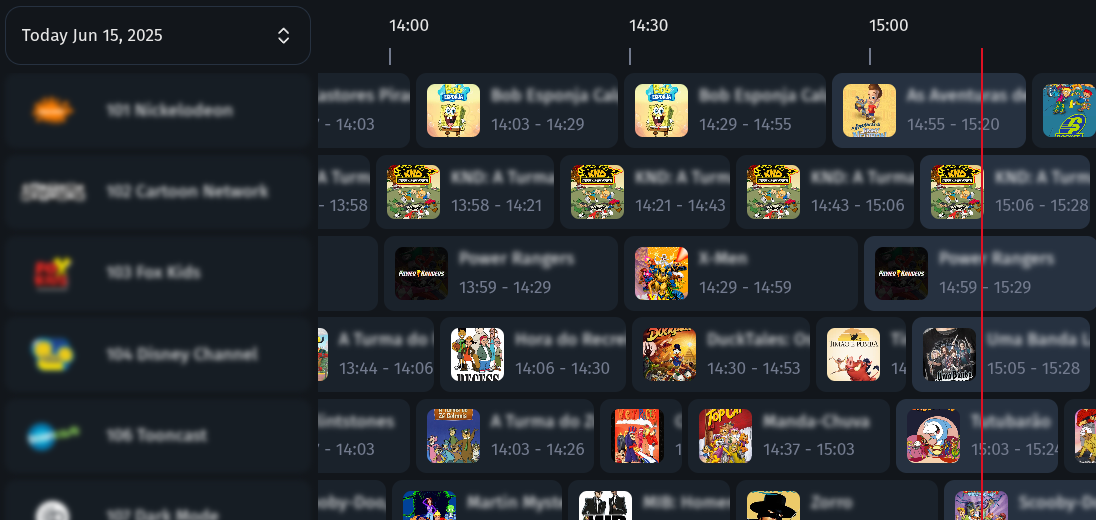
ErsatzTV lets you transform your media library into a personalized, live TV experience - complete with EPG, channel scheduling, and seamless streaming to all your devices. Rediscover your content, your way.


How It Works
- Install ErsatzTV: Download and set up the server on your system.
- Add Your Media: Connect your media libraries and collections.
- Create Channels: Design and schedule your own live channels.
- Stream Anywhere: Watch on any device with IPTV and EPG support.
Key Features
- Custom channels: Create and schedule your own live TV channels.
- IPTV & EPG: Stream with IPTV and Electronic Program Guide support.
- Hardware Transcoding: High-performance streaming with hardware acceleration (NVENC, QSV, VAAPI, AMF, VideoToolbox)
- Media Server Integration: Connect Plex, Jellyfin, Emby and more.
- Music & Subtitles: Mix music videos and enjoy subtitle support.
- Open Source: Free, open, and community-driven project.
Documentation
Documentation is available at ersatztv.org.
License
This project is inspired by pseudotv-plex and the dizquetv fork and is released under the zlib license.